A browser agent can work through the same screens a person uses: reading pages, clicking buttons, filling forms, collecting reports, and moving between business tools. That makes it useful for QA, research, administrative checks, ecommerce reviews, support preparation, and sales operations.
Write down the task, account session, accessible data, permitted actions, review point, log, owner, and rollback path. That gives the team a way to distinguish approved help from work it will have to undo.
What is a browser agent operating model?
A browser agent operating model is the rule set for an AI agent working inside websites and business apps. It defines the account it uses, the pages it can see, the fields it can change, the moments that require approval, and the evidence the business can inspect afterward.
Browser agents close the distance between advice and action. A normal assistant may suggest an email reply. A browser agent may open the CRM, read the account, draft the reply, update the status, and prepare the follow-up task. The speed is useful; the risk now travels through the same workflow.
OpenAI's computer use guidance tells developers to run computer using agents in isolated environments and to require user confirmation before consequential actions. That is the right business principle too. Do not give a browser agent a normal employee session and hope prompting is enough.
Which browser agent tasks are safe enough to start with?
The safest first tasks are read only, reversible, or draft based. A business can ask a browser agent to test a lead form, compare public pages, collect screenshots, check product fields, pull a report, or draft a CRM note. Those jobs still need boundaries, but the damage from a bad step is easier to catch.
The risky tasks are the ones that affect customers, money, access, inventory, legal records, public pages, or account status. Those can be useful later, but they need stronger gates. A browser agent should not refund an order, invite a user, change pricing, publish a page, or send a customer email unless the approval and trace model is already working.
| Task type | Good first use | Main risk | Required control |
|---|---|---|---|
| Read only checks | Collect page state, reports, screenshots, or public facts | Private data exposure | Scoped account and redaction rule |
| Draft work | Create CRM notes, support replies, page edits, or QA findings | Bad draft accepted too quickly | Human approval before send or publish |
| Form testing | Check lead forms, checkout forms, booking flows, and support intake | Test data enters production | Test account, marker values, and cleanup step |
| Internal updates | Move tasks, tag records, update non customer fields | Wrong record changed | Preview diff and reviewer approval |
| Customer or money actions | Only after the trace model has proven reliable | Customer harm, dispute, or security event | Explicit approval, limits, and rollback owner |
Why is a normal logged in browser session risky?
Your everyday browser can be a loaded key ring: customer records, billing, admin menus, saved passwords, chats, documents, inboxes, ad accounts, analytics, and support. Giving an agent the whole session can make much more available than its job requires.
That is why the session should be designed for the job. Use a test store when testing checkout. Use a read only CRM role when collecting account context. Use a staging site for page changes. Use a fresh browser profile when the job does not need the user's normal cookies. Use a demo account when the agent only needs to prove a workflow pattern.
Use authentication where the task needs it, with a session scoped to that task. Keep evidence that the agent used only the permitted access.
How do AI visibility and agent friendly websites fit in?
Browser agents are also changing what it means for a website to be usable. A site can rank, load, and look fine for a person while still being hard for an agent to understand. Google (GOOG) has published guidance on building agent friendly websites that calls for clear purpose, semantic HTML, accessible controls, predictable flows, and machine readable context.
That advice connects SEO, AEO, GEO, and operations. Search engines need to understand your pages. Answer engines need clear facts and citations. Browser agents need stable labels, forms, buttons, page state, and proof that the action they are about to take is the right one.
Cloudflare (NET) has also been pushing signed agent and Web Bot Auth work. That points to the same future from the access side: businesses will need to tell useful agents apart from generic automation, crawlers, scrapers, and risky traffic. Visibility and access policy will meet in the same operating plan.
What should the approval ladder look like?
Approval should rise with consequence. A browser agent can gather public facts with little friction. It should ask before editing an internal record. It should require explicit approval before any customer facing message, public page update, access change, billing action, refund, order edit, or legal record change.
Show the reviewer the current record, proposed change, source, reason, confidence, affected system, and rollback path. 'Approve action' alone does not give them enough information to decide.
What should the log capture?
The log should be useful after something goes wrong. Store the task, account, start time, pages visited, key fields read, proposed action, final action, skipped action, reviewer, approval time, and rollback note. For sensitive systems, store enough evidence to audit behavior without copying private data into the wrong place.
Logs also help improve the agent. If a browser agent fails because a page changed, label moved, auth expired, field was hidden, or data was ambiguous, the fix may be product design, source cleanup, or a better review rule rather than a new prompt.
What risks should operators watch first?
OWASP's 2026 Top 10 for Agentic Applications lists risks such as memory poisoning, tool misuse, privilege compromise, resource overload, and misaligned behavior. Those sound technical, but they show up in ordinary business workflows.
A browser agent can read a page with misleading instructions. It can use a tool too broadly. It can inherit a permission it should not have. It can keep retrying a failing task until it creates noise. It can complete the literal task while violating the business intent. The operating model needs to account for those failures before the agent gets wider access.
How should a business roll this out in 30 days?
Start with one workflow that is useful but bounded. Do not begin with the highest risk action. Pick a task where a person already wastes time checking a web app and turning findings into a draft or internal record.
- Choose one browser task and define success in plain language.
- Create a safe account or browser profile for that task.
- List the pages, fields, and actions the agent may use.
- Block customer, money, access, and public page actions at first.
- Run ten sample tasks and inspect the trace.
- Write the approval screen around the real reviewer decision.
- Add a rollback owner for every action that changes state.
- Move one permission upward only after the lower step is boring.
Use the pilot to establish that one workflow produces useful work, leaves an inspectable record, and can recover from mistakes before expanding its scope.
Where should product and marketing teams help?
Product teams should make important flows easier for both people and agents. Use real labels, stable form fields, clear validation messages, accessible controls, predictable redirects, visible status, and clean error states. If the agent has to guess what a button does, a user probably has to guess too.
Marketing and SEO teams should make public proof clear. Keep service pages, case studies, product pages, reviews, directories, docs, support pages, and structured data consistent. If an answer engine or browser agent sees conflicting claims, it has less reason to trust the action path.
This is where the citation environment matters. AI tools are more likely to trust a business when owned pages, public profiles, reviews, docs, and customer language tell the same story. A browser agent may be acting in a web app, but the confidence behind that action often comes from the public record around the business.
Where to go next
If you are still choosing the first workflow, read the Deploy Agentic guide to AI agent workflow automation. If the agent needs narrow tools and ongoing maintenance, use the dedicated AI agents guide. If the website itself needs to become easier for agents to read and use, pair this with agent ready websites and WebMCP.
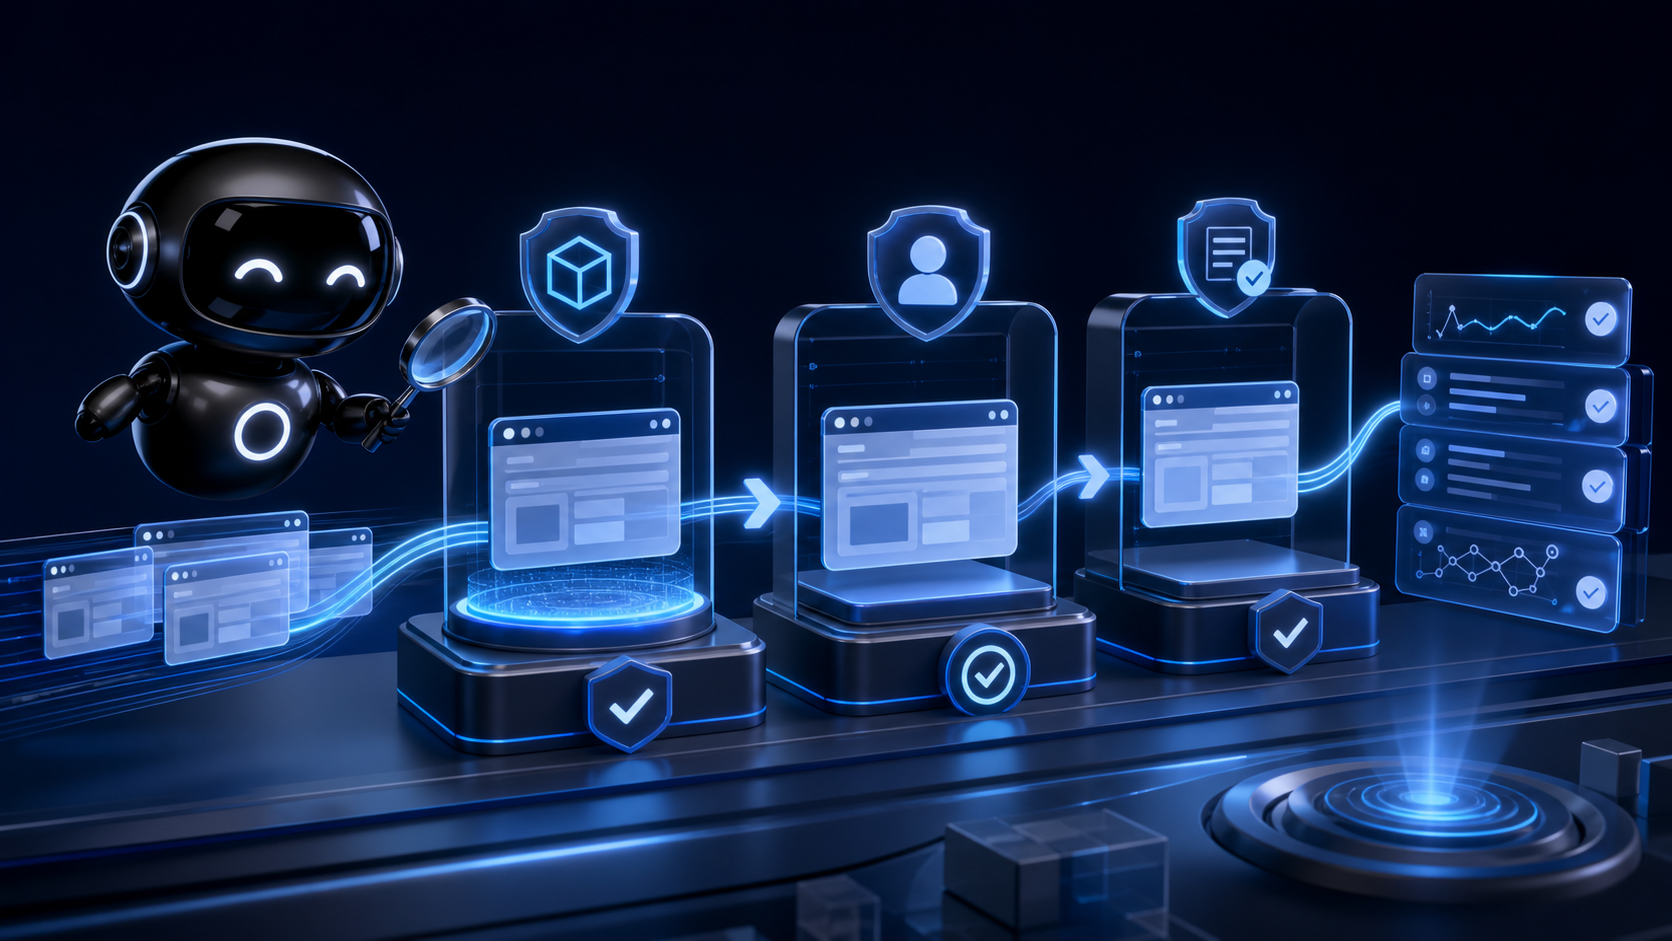
Deploy Agentic maps browser agent work as an operating loop: safe session, task boundary, review gate, action trace, rollback, and quarterly refresh. The contact page is the cleanest next step if you want to test one browser agent workflow without exposing real systems too early.
FAQ
What is a browser agent operating model?
It is the rule set for how an AI agent can work inside websites and business apps. It defines safe sessions, approved tasks, permissions, review gates, logs, rollback, and ownership.
Should browser agents use a normal employee login?
No. Start with isolated accounts, demo accounts, staging sites, scoped browser profiles, or read only roles. A normal employee session often exposes more data and authority than the agent needs.
Which tasks are safest for browser agents?
Read only checks, QA, report collection, draft creation, form testing, and internal research are the best first tasks. Customer messages, refunds, access changes, inventory changes, and public page updates need stronger approval.
How do browser agents affect AI visibility?
They make usability part of AI visibility. Clear labels, semantic HTML, structured data, current proof, and consistent public facts help agents understand what a business offers and what actions are safe to take.
Sources
- OpenAI documentation: Computer use tool
- OpenAI documentation: Agents
- OpenAI documentation: Guardrails and approvals
- web.dev: Build agent friendly websites
- Google Search Central: AI features and your website
- Cloudflare documentation: Signed agents
- Cloudflare documentation: Web Bot Auth
- OWASP: Top 10 for Agentic Applications
- NIST AI Risk Management Framework
- Schema.org: Article type
- Schema.org: FAQPage type
Test one browser agent workflow before expanding access
Deploy Agentic can map the safe account, approved actions, review gates, trace records, and rollback path for a browser agent that works inside your real operating stack without starting with full access.
Plan a browser agent pilot